Simplify Cybersecurity
Governance, Risk & Compliance
Protect your infrastructure with eGCESM, an advanced cybersecurity pre-assessment GRC platform. It evaluates your business process controls against leading global and regulatory standards—including ISO, NIST, PCI DSS, GDPR, HIPAA, and regional frameworks—to identify security gaps and defend your enterprise from cyber threats.
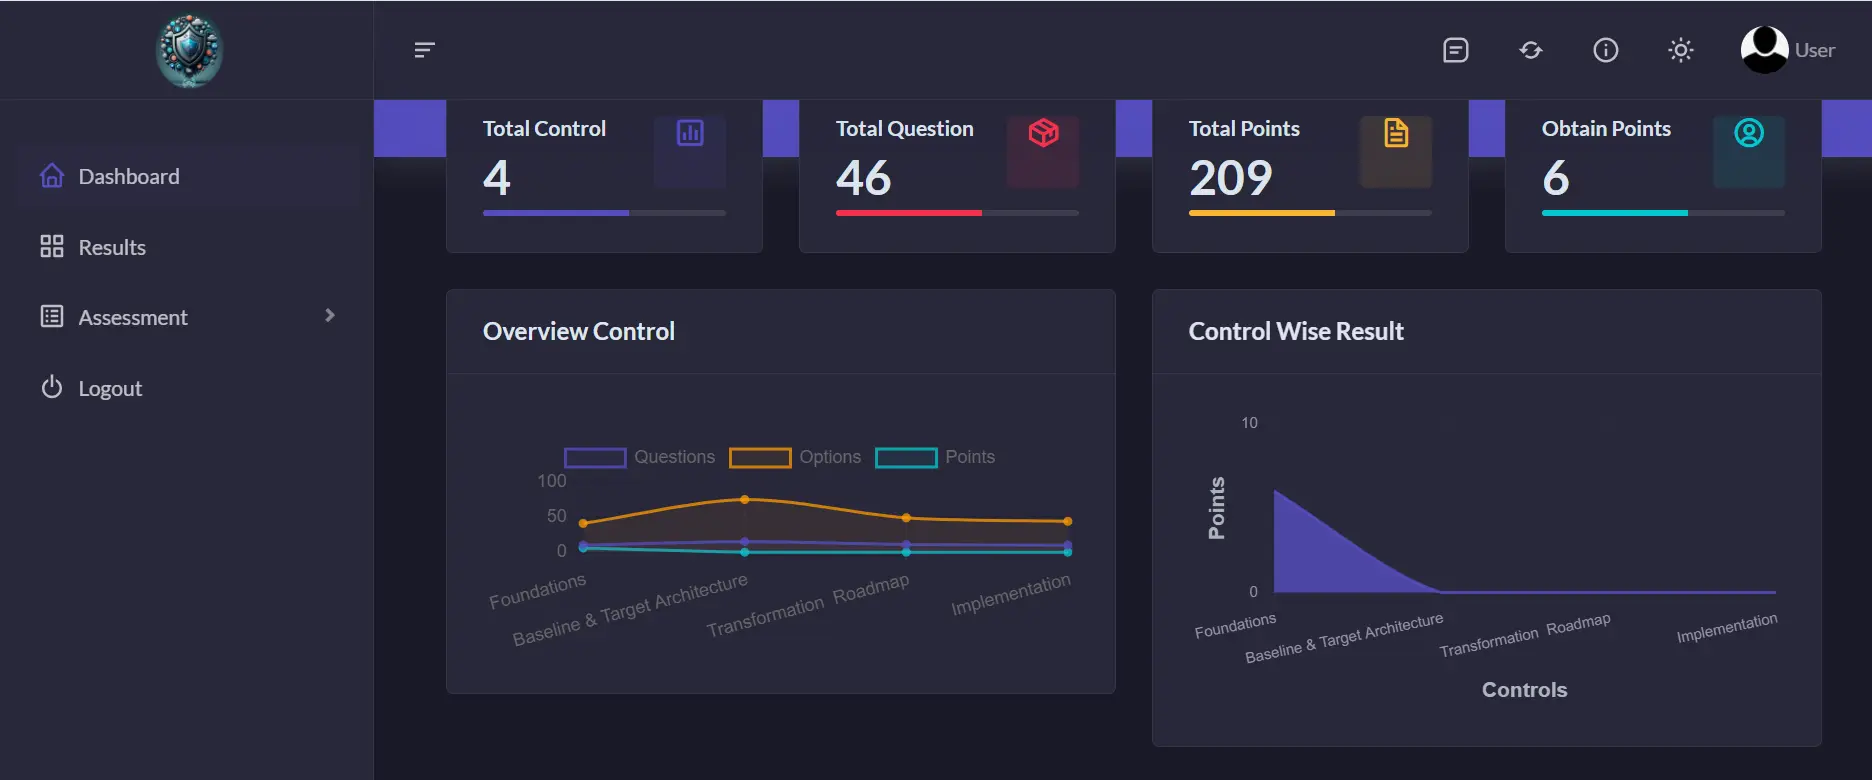
Built Around Global Compliance Frameworks
Assess your organization's cybersecurity posture against internationally recognized governance, risk, and compliance frameworks.
Easy Assessment Flow — Questionnaire to Report
Complete your assessment in 5 simple steps and get instant audit-ready reports.
Select Framework
Answer Questionnaire
Instant Point Calculation
Risk & Maturity Analytics
Export PDF & Excel Reports
Select Framework
Choose your target compliance framework (e.g., TOGAF, ISO) and see total controls, questions, and points.
Powerful Features to Boost Your
Security Governance
Stay ahead with automated compliance features built for performance, risk visibility, and enterprise scale.
Assessment Management
Create, manage and execute compliance assessments with structured workflows.
Multi-Framework Support
ISO, NIST, CIS, GDPR, HIPAA, PCI DSS and more out of the box.
Role-Based Access Control
Secure user roles, customizable permissions, and access governance.
Audit Management
Plan, approve and track audits efficiently with audit trail history.
Reporting & Dashboards
Interactive dashboards, real-time charts, PDF and Excel exports.
Governance & Compliance
Centralized governance, risk mapping and compliance workflows.
Everything You Need in One Single Platform
eGCESM combines governance, cybersecurity assessment and compliance management into a unified enterprise platform.
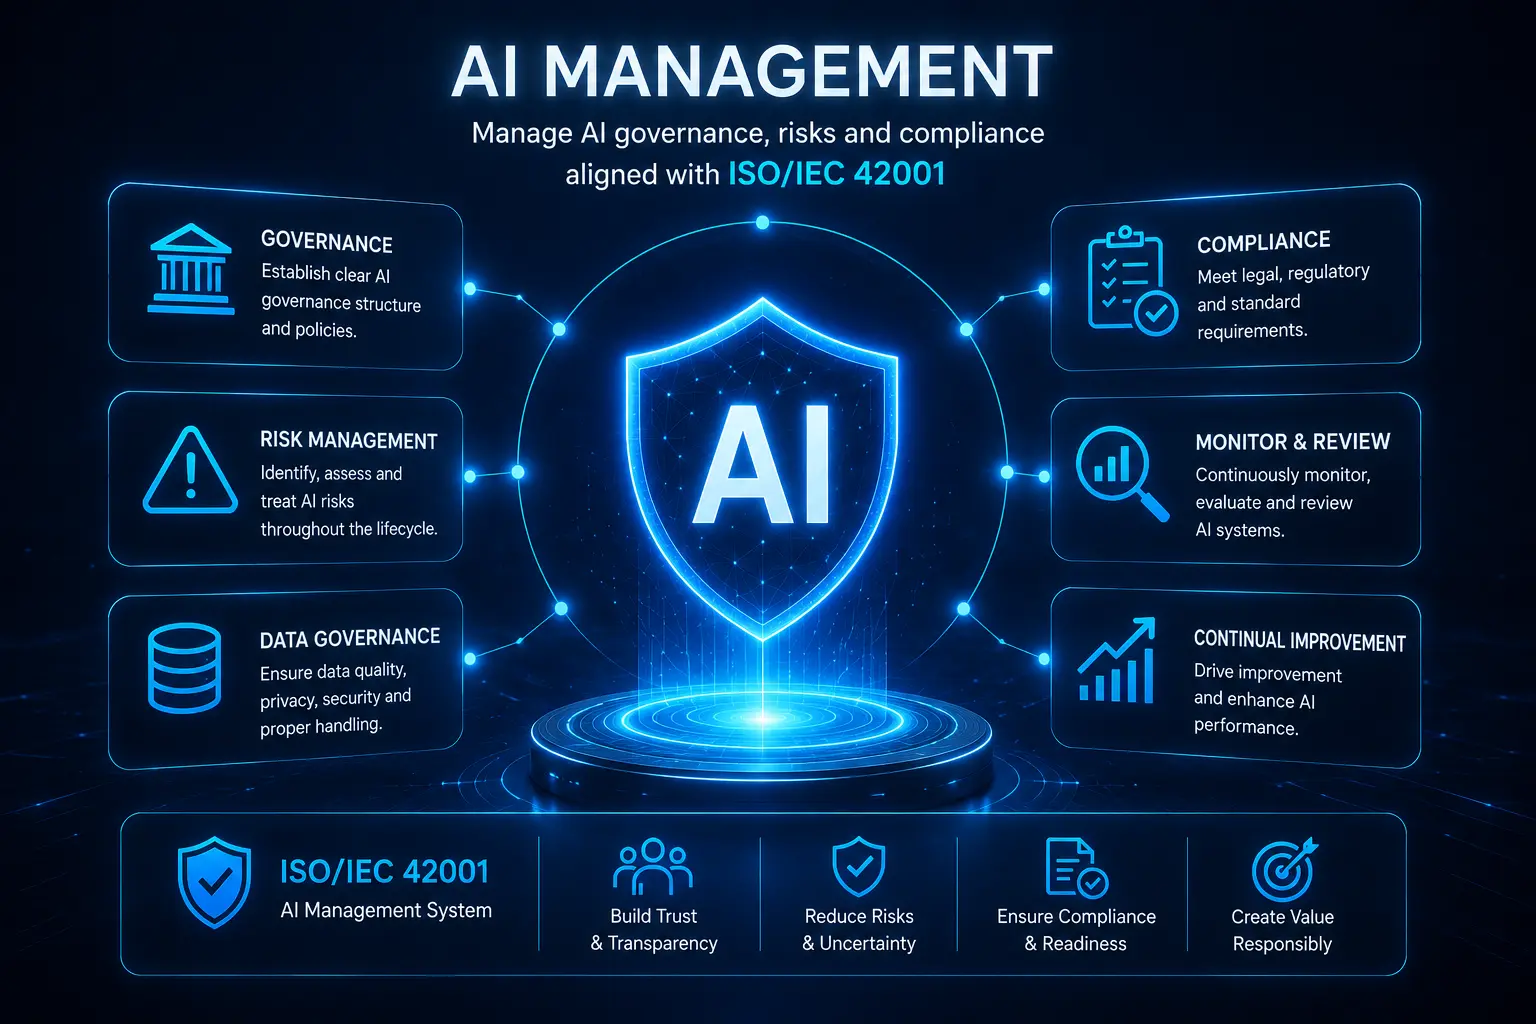
AI Management
Manage AI governance, risks and compliance aligned with ISO/IEC 42001.
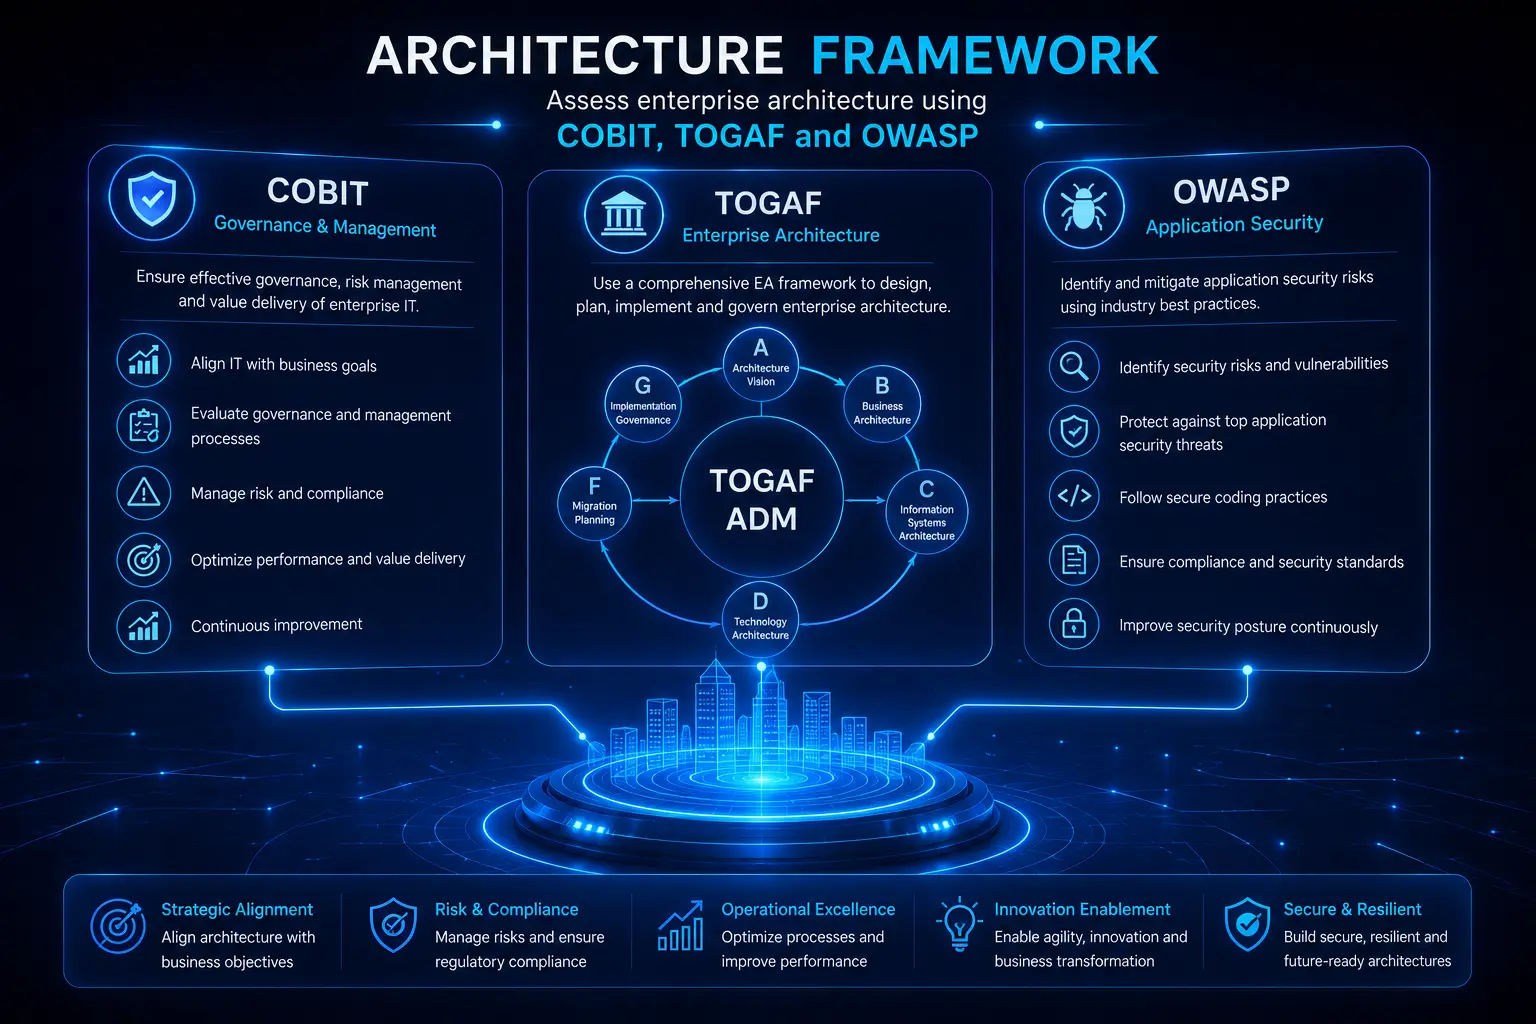
Architecture Framework
Assess enterprise architecture using COBIT, TOGAF and OWASP.
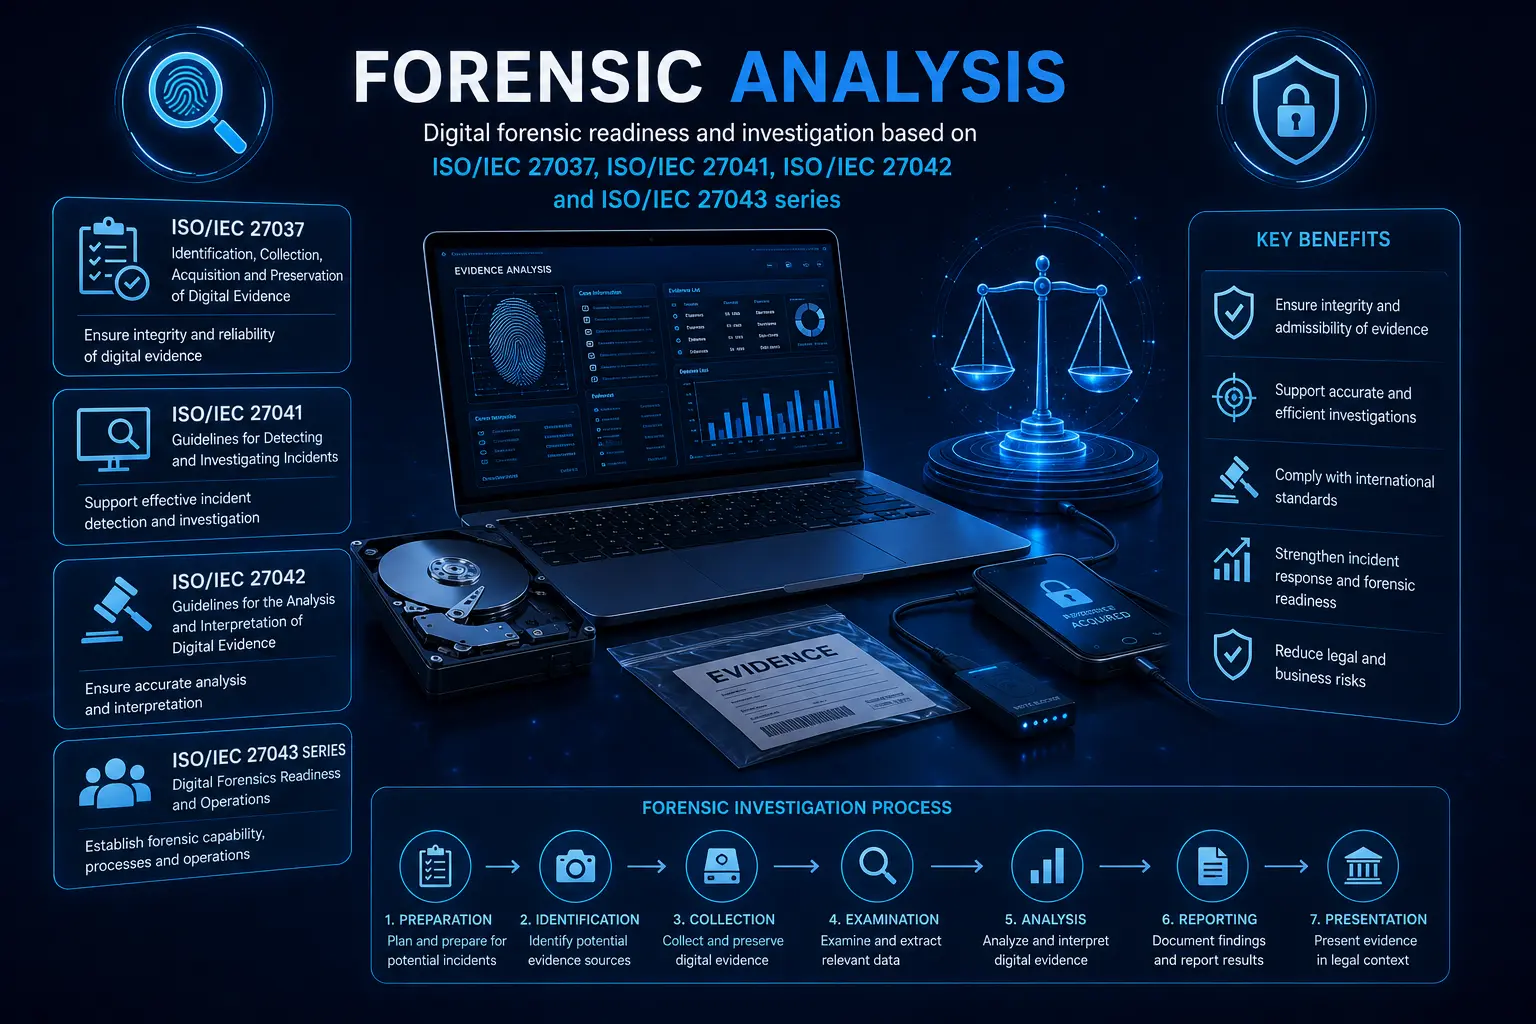
Forensic Analysis
Digital forensic readiness and investigation based on ISO IEC 27037, ISO IEC 27041, ISO IEC 27042 and ISO IEC 27043 series.
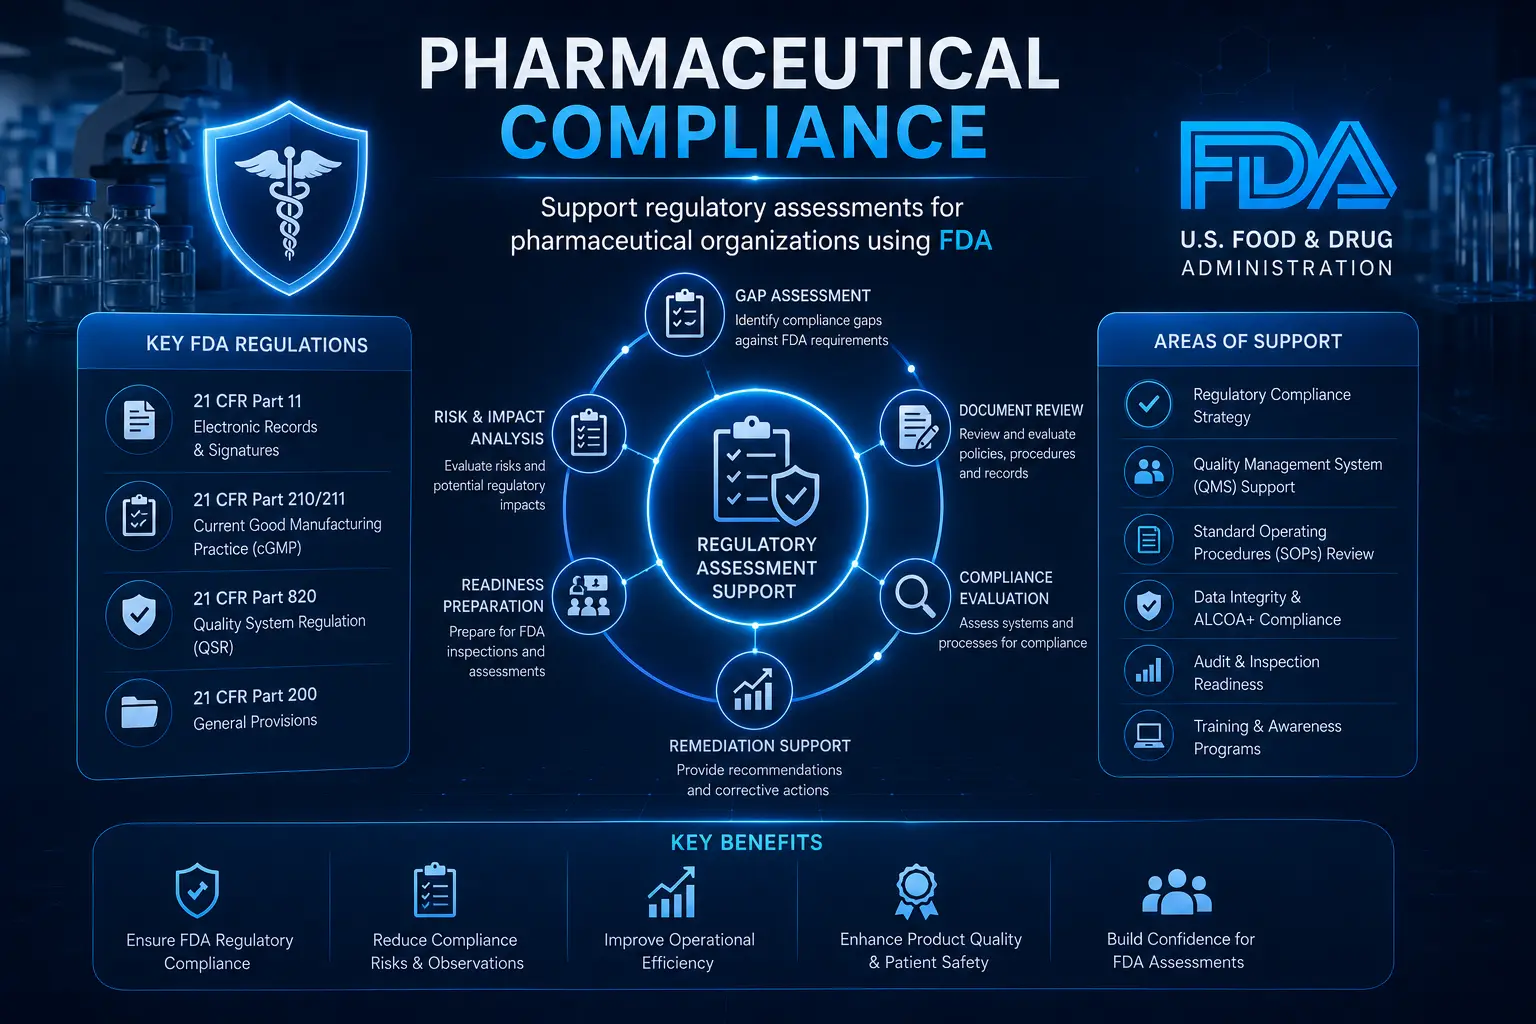
Pharmaceutical Compliance
Support regulatory assessments for pharmaceutical organizations.
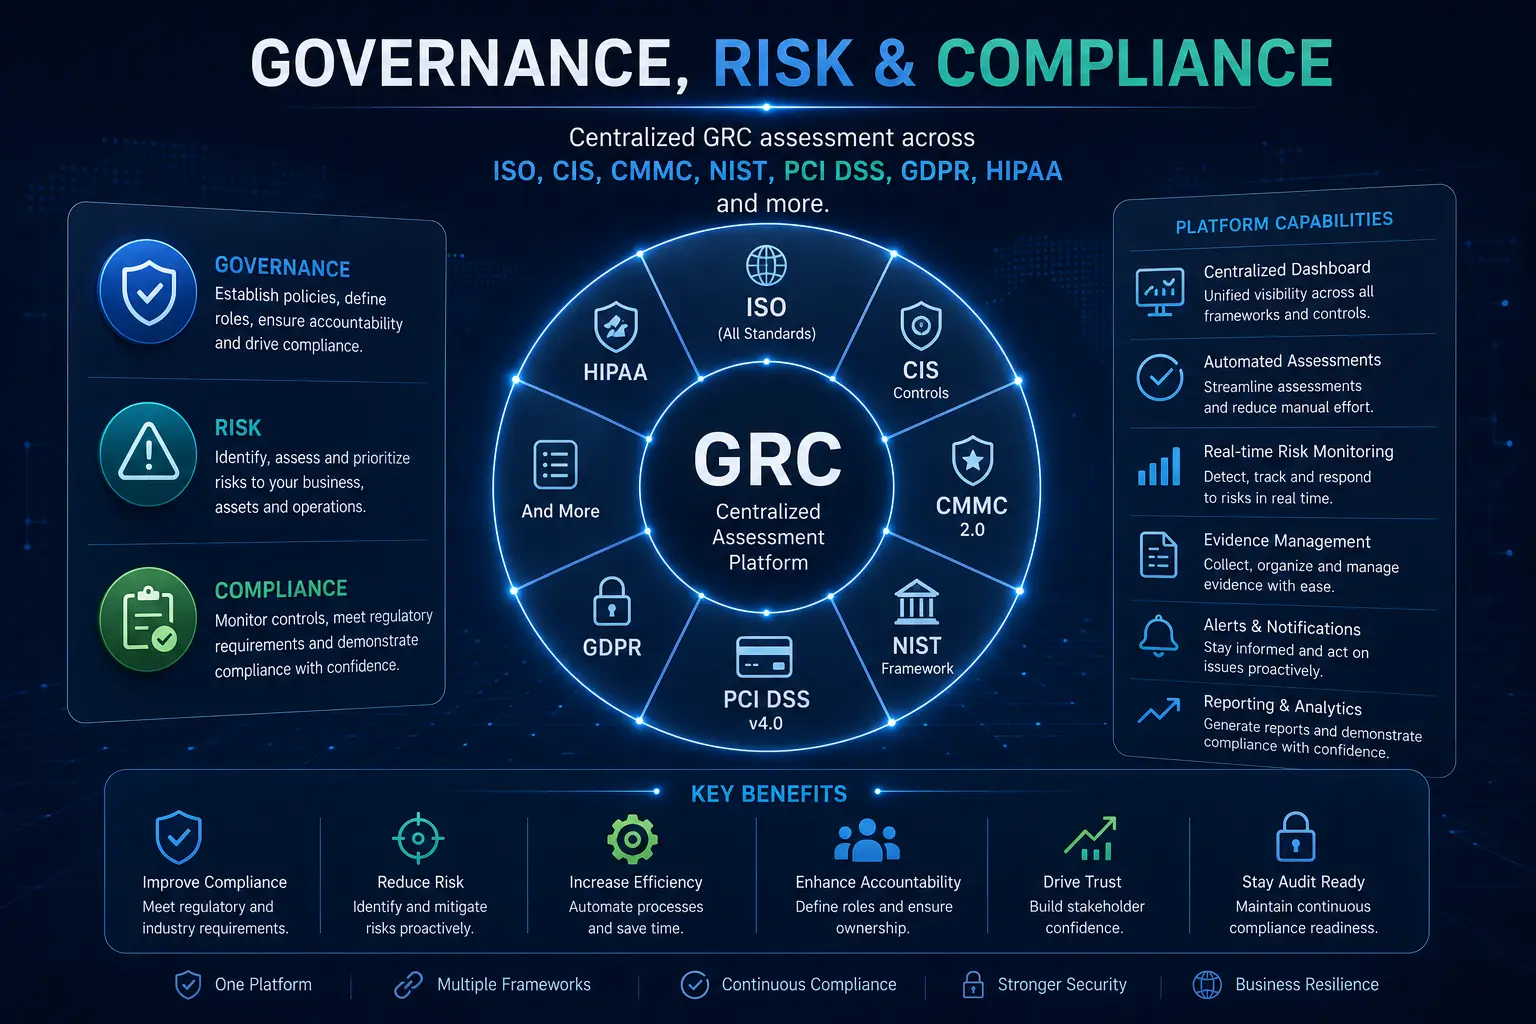
Governance, Risk & Compliance
Centralized GRC assessment across ISO, CIS, CMMC, NIST, PCI DSS, GDPR, HIPAA and more.
Tailored Compliance for Every Industry
eGCESM scales to meet the unique governance, risk, and regulatory demands of highly regulated sectors.
Banking & Financial Services
Ensure PCI-DSS and SWIFT compliance while protecting sensitive financial data and transaction systems.
Healthcare & Life Sciences
Safeguard patient records (PHI) and simplify HIPAA & GDPR compliance across health platforms.
Government & Public Sector
Align critical infrastructure with NIST, ISO 27001, and national cybersecurity standards.
Telecommunications
Protect high-volume network infrastructure and user data against global threat actors.
Energy & Utilities
Secure operational technology (OT) and critical infrastructure from cyber disruptions.
Pharmaceuticals
Maintain strict governance, IP protection, and regulatory compliance for medical research.
Frequently Asked Questions
Find answers to common questions about the eGCESM platform.
eGovernance Cognitive Enterprise Security Manager (eGCESM) is an enterprise cybersecurity pre-assessment and Governance, Risk & Compliance (GRC) platform that helps organizations evaluate their security posture against international standards.
Strengthen Your Cybersecurity Compliance with eGCESM
Discover security gaps, assess compliance, and generate enterprise-grade reports using internationally recognized cybersecurity frameworks.